

DNIF
Cloud-native SIEM, UEBA and SOAR platform for organisations with very large volumes of security data
- User Activity Monitoring
- 24/7 (Live Rep)
- Online
- Business Hours
- +13 more

About DNIF
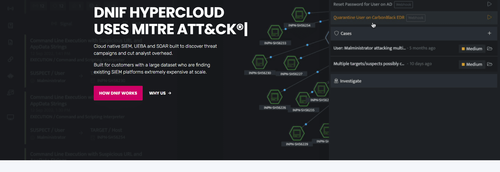
DNIF is a cloud-native security platform that merges SIEM, user behaviour analytics and SOAR in one product. Its HYPERCLOUD edition targets customers whose data volumes make conventional SIEM tools expensive to run.
What DNIF offers
- Large-scale ingestion — collects, enriches, stores and correlates security data at very high volumes.
- Threat campaign detection — uses machine learning and graph analytics to group many alerts into a few campaigns.
- Search and analytics — a native query language or a graphical query builder, plus pipelines for multi-stage use cases.
- ATT&CK mapping — threat content is aligned with the MITRE ATT&CK framework.
- Automation — prebuilt integrations and playbooks, with case management that tracks progress through the kill chain.
Who it works with
Security operations centres, including multi-tenant setups with role-based access control.
Key facts
- Data retention: all events stay immediately searchable for 365 days
- Integrations: cloud providers, security devices, operating systems and applications
Profile written by TrustList from the business's own published information, Oct 2026.
Gallery
2 images — click to enlarge
Categories & features
- User Activity Monitoring
- 24/7 (Live Rep)
- Online
- Business Hours
- Documentation
- Webinars
- Web-Based, Cloud, SaaS
- Installed - Windows
- AI/Machine Learning
- Real Time Monitoring
- Threat Intelligence
- Log Management
- Forensic Analysis
- Whitelisting/Blacklisting
- Incident Management
- Compliance Reporting
- Behavioral Analytics
Rankings
- Siem software › Installed windows#5
- Siem software › Behavioral analytics#6
- Siem software › Compliance reporting#6
- Siem software › Log management#6
- Siem software › Forensic analysis#6
- Siem software › Real time monitoring#7
- Siem software › Threat intelligence#7
- Siem software › User activity monitoring#7
- Siem software › Web based cloud saas#8
- Incident management software#31
As of 2026-10-05. Organic ranks only; sponsored placements are never ranks.
Request a demo or quote from DNIF
Reviews
Questions & answers
No questions yet. Be the first to ask about DNIF.
DNIF alternatives
Similar listings buyers compare against this one.


Security monitoring software from IBM that detects and ranks network threats using machine learning


Cloud security analytics platform combining SIEM, user behaviour analytics and incident response automation


Open source SIEM and XDR platform for threat detection, log management and compliance reporting


Security monitoring platform that analyses agent data against threat intelligence for real-time visibility

SIEM platform that correlates log events into alerts, on premises or in the cloud
Related reading
Articles that share the User Activity Monitoring tag or mention this listing.
 Log Management
5 Oct 2026
Cloudflare opens Logpush to Free, Pro and Business plans with usage-based pricing: 25 GB included, then $0.03 to $0.10 per GB
Cloudflare Logpush is now available on all plans with usage-based charges: 25 GB a month of internal or external exports included, then…
 United States
5 Oct 2026
Google Cloud's legacy Monitoring and Logging agents reached end of support on 28 September 2026: migrate to the Ops Agent
Google Cloud's legacy Monitoring and Logging agents reached end of support on 28 September 2026: no new versions and no standard…
 Cybersecurity
2 Oct 2026
FortiMail flaw CVE-2026-104286 is exploited and fixes are still upcoming: disable IBE or close the management interface now
Fortinet says CVE-2026-104286, an unauthenticated file-write flaw in FortiMail rated 9.8, is exploited in the wild. Fixed builds 8.0.2,…
More on TrustList
Everything here links back to the same verified catalogue. Pick your next stop.
- More User Activity MonitoringBack to the ranked category
- Write a reviewHelp other buyers decide
- CompaniesAgencies, consultancies and IT service providers, ranked by verified reviews.
- ArticlesGuides, comparisons and research from the editorial desk and the community.
- AwardsAnnual recognition decided by verified reviews and an independent jury.
- LaunchesNew products and releases, voted up by the community every day.
- AI ModelsBenchmark scores and community ratings for every major model.
- RequestsBuyers describe what they need; vendors respond directly.
- PeopleReviewers, authors and makers with public profiles.
- ComparePut up to four listings side by side before you shortlist.