


Micro Focus tool for spotting internal and external security threats through user behaviour analytics

AWS service that records and checks the configuration of cloud resources for audit and compliance
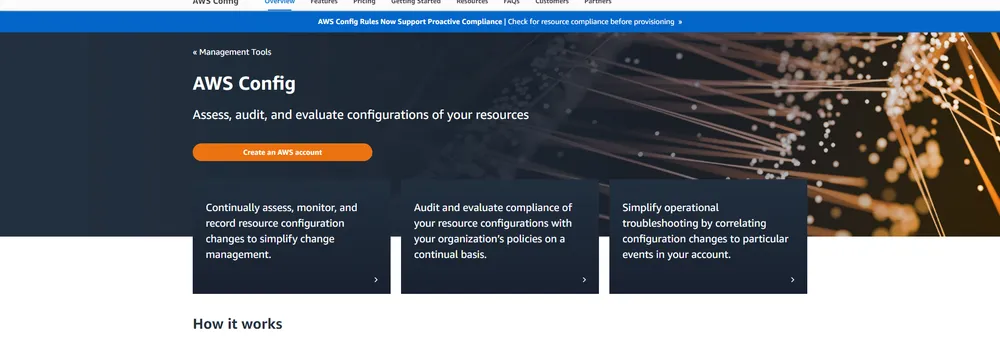
Amazon Config, sold by Amazon Web Services under the name AWS Config, assesses, audits and evaluates how cloud resources are configured. It finds the resources an account holds, logs their configurations and captures each change, so teams can review what changed and when. It also tracks the relationships between resources, and the company notes that third-party resources can have their configuration data published into it.
Recorded settings are compared with an organization's policies on a continuing basis. Rather than a one-off review, configurations are monitored and evaluated automatically against the state the organization wants, which gives auditors and administrators a running picture of compliance.
Compliance requirements can be codified as Config rules, and remediation actions can be written to correct any failing resource. Once the rules are in place, the assessment runs across the whole organization, so each account is held to the same standard without a manual check each time.
Operational troubleshooting is simplified by linking configuration changes to particular events in an account. Teams can see what changed just before a fault appeared, which speeds up the work of finding the cause.
Resource configurations are evaluated for potential vulnerabilities, and the configuration history can be reviewed after an incident to examine the security posture as it was at the time. The company's pages also name third-party software risk assessments as a use case, in line with the audit and governance work the service supports.
Amazon Config, sold by Amazon Web Services as AWS Config, tracks how cloud resources are set up. It discovers resources in an account, records their settings and keeps a history of every change.
Organisations running workloads on AWS that must audit, govern or troubleshoot their environments, including those assessing third-party software risk.
Summary written by TrustList from the business's own published information, Nov 2026.
2 images - click to enlarge
Used it? Your experience helps other buyers decide.
Write a reviewNo questions yet. Be the first to ask about Amazon Config.
Similar listings buyers compare against this one.
Micro Focus tool for spotting internal and external security threats through user behaviour analytics

Application security testing platform from High-Tech Bridge covering web and source code vulnerabilities

Security orchestration and automation platform that coordinates incident response across a company's security tools

Web application and external attack surface security scanner for security and development teams

Software composition analysis tool that finds and controls open source risk across the development lifecycle

Cloud-based vulnerability management that scans networks, analyses risk and reports through continuous monitoring

Unified security management platform for threat detection and compliance in mid-size organisations

Developer-focused security platform that finds and fixes vulnerabilities in code, dependencies and containers
The newest guides and analysis from TrustList Insights.
 Brazil
22 Nov 2026
Receita Federal has opened the restricted CBS pilot environment to all companies without prior request, and has sent the accounting council…
 South Africa
22 Nov 2026
SARS matched National Treasury payments against nil VAT returns from Central Supplier Database suppliers, found 14,142 nil-return periods…
 United States of America
22 Nov 2026
OpenRouter has off-boarded three inference providers and removed 125 endpoints from Zero Data Retention after Dragos seeded about two…
Everything here links back to the same verified catalogue. Pick your next stop.


