


eZReview Your All-in-one eDiscovery Solution

OSForensics Digital investigation for a new era
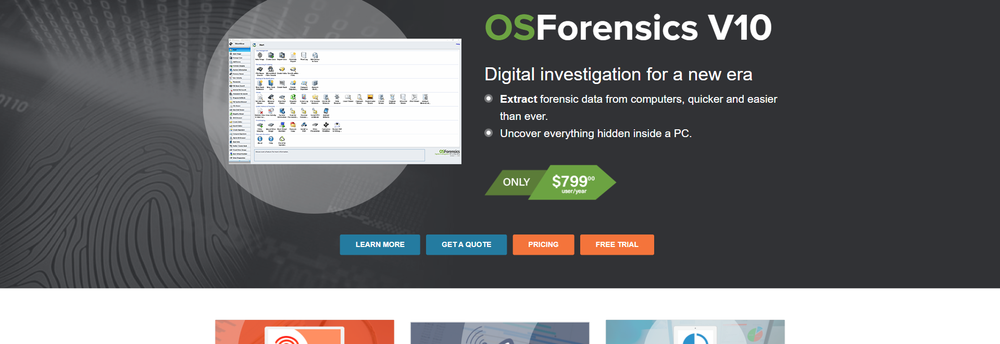
Discover relevant data faster through high performance file searching and indexing Extract passwords, decrypt files and recover deleted files quickly and automatically from Windows, Mac and Linux file systems
Identify evidence and suspicious activity through our hash matching and drive signature analysis features Identify and analyze all files and even automatically create a timeline of all user activity
360° Case Management Solution Manage your entire digital investigation with OSF’s new reporting features Build custom reports, add narratives and even attach your other tools’ reports to the OSF report
Discover relevant data and evidence faster through high performance file searching
Mount local disk image files in Windows as a physical disk or a logical drive letter
A self-booting solution which enables you to create or clone exact raw disk images
OSForensics courses offered to suit a diverse range of users and skill sets
Volatility Workbench is a graphical user interface (GUI) for the Volatility tool
Write an image concurrently to multiple USB Flash Drives
October 5 - 7, 2022 Redmond, Washington December 12 - 14, 2022 Orlando, Florida See our full schedule of conferences and events for the year
2 images — click to enlarge
Used it? Your experience helps other buyers decide.
Write a reviewNo questions yet. Be the first to ask about OSForensics.
Similar listings buyers compare against this one.
eZReview Your All-in-one eDiscovery Solution

Concordance Reduce risk with data on demand and find the answers you need quickly.

Page Vault WEB CAPTURES FOR LEGAL PROFESSIONALS
The newest guides and analysis from TrustList Insights.
 Artificial Intelligence News
14 Sept 2026
Of eleven business launches that ranked on 8–10 September, four put a human approval step at the centre of the product — and seven were…
 Artificial Intelligence News
12 Sept 2026
84 launches in 30 days: 14 AI models, and 21 tools to route, govern and meter calls to them.
 Artificial Intelligence News
12 Sept 2026
OpenAI, Sakana AI and DeepSeek all shipped in the same four days. Every release was a pricing decision wearing a model announcement.
Everything here links back to the same verified catalogue. Pick your next stop.


